AI Governance for IT Teams: How to Balance Control & Innovation
Category:: Artificial Intelligence (AI)

Artificial intelligence is becoming part of everyday IT operations, from software development and customer support to data analysis, cybersecurity, and business automation. As adoption grows, organizations need clear ways to manage the selection, development, deployment, and monitoring of AI.
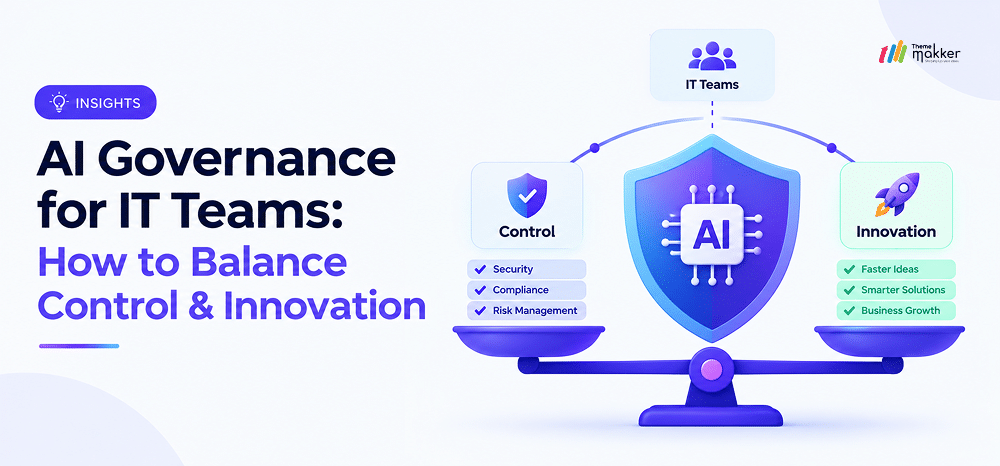
The challenge is maintaining responsible oversight without creating unnecessary delays. Excessive approval requirements can discourage experimentation, while limited oversight can increase risks to security, privacy, compliance, and quality.
A practical approach to AI governance creates clear expectations while allowing IT teams to continue experimenting and delivering solutions at speed.
The goal is not to control every AI activity, but to create a system in which teams understand what they can do independently and when additional review is required.
Why AI Governance Matters for IT Teams
Managing the Risks That Come With AI Adoption
AI systems can process sensitive information, influence business decisions, communicate with customers, and automate important processes. Without clear oversight, different teams may adopt AI applications without fully understanding their risks.
Governance gives organizations a structured way to address concerns involving data protection, security, privacy, reliability, transparency, and accountability. It also creates a consistent approach to evaluating AI initiatives across departments.
Balancing Innovation With Responsible Oversight
IT teams need room to experiment. Requiring senior approval for every AI experiment can unnecessarily slow development. At the same time, allowing unrestricted AI usage can expose organizations to serious operational and compliance problems.
The solution is proportional oversight. Low-risk activities should have simple requirements, while systems that affect customers, employees, finances, or sensitive information should receive greater scrutiny.
This approach allows teams to move quickly while ensuring that higher risk applications receive appropriate attention.
Building an AI Governance Framework That Supports Delivery
1. Creating Risk-Based Approval Processes
An AI governance framework should define how an AI initiative moves from an idea to production. It should establish who approves projects, what information can be used, what testing is required, and what happens when a system produces unexpected results.
A useful starting point is to classify AI projects according to their potential impact. Factors can include data sensitivity, number of users, business importance, customer exposure, and potential consequences of incorrect outputs.
For example, an internal writing assistant may require basic security and privacy checks. An AI system that influences employee recruitment or financial decisions may require significantly stronger review.
2. Making Governance Proportional to Risk
Not every AI project deserves the same level of oversight. A simple classification system can prevent governance from becoming a bottleneck.
IT teams can establish categories such as low, medium, and high risk. Each category can have predefined requirements covering documentation, testing, approval, monitoring, and review.
This means developers do not have to wait for extensive approvals when working on low-risk projects. At the same time, important systems receive the attention they require before reaching users.
Defining AI Governance Roles and Responsibilities
1. Assigning Ownership Across the AI Lifecycle
Clear AI governance responsibilities are essential because AI systems involve multiple teams. Developers, security professionals, business leaders, legal teams, and data specialists may all have different responsibilities.
Developers can oversee technical quality and testing. Security teams can assess security risks and access controls. Legal and compliance teams can review applicable requirements. Business owners can remain accountable for how an AI system is used.
Clearly assigning these responsibilities reduces confusion and prevents important tasks from being overlooked.
2. Creating Clear AI Governance Roles
Well-defined AI governance roles can also speed up decision-making. Instead of creating a new approval group for every AI project, organizations can assign responsibilities to existing teams and establish clear escalation points.
For example, developers may handle routine technical checks, while security or compliance teams become involved only when predefined risk conditions are met.
Ownership should continue after deployment. Someone must remain responsible for monitoring the system, reviewing incidents, managing significant changes, and deciding when the system needs improvement or retirement.
Applying AI Governance Best Practices in Daily Development
1. Establishing Clear Rules for AI Usage
Effective AI governance best practices should be simple enough for employees and developers to understand. Organizations should clearly explain which AI applications are approved, what information can be entered into them, and when employees need additional permission.
Clear guidance is particularly important when teams use publicly available AI services. Employees may unknowingly share confidential business information if they do not understand the organization’s rules.
2. Making Documentation Simple and Useful
Documentation does not need to become a lengthy administrative exercise. IT teams can maintain a basic record containing the purpose of an AI system, its owner, the information it processes, its expected users, known limitations, and important controls.
This information provides decision-makers with sufficient visibility without forcing development teams to spend excessive time preparing paperwork.
3. Making Testing Part of the Development Process
AI systems should be tested before they are introduced to users. Testing can examine accuracy, reliability, security, privacy, and the possibility of inappropriate results.
The level of testing should reflect the potential impact of the system. A simple internal application may need limited testing, while an AI system involved in important business decisions requires more extensive evaluation.
4. Monitoring AI Systems After Deployment
Governance should continue after an AI system goes live. Changes in models, data, integrations, or user behavior can affect performance over time.
Regular reviews can help organizations identify inaccurate results, unexpected behavior, security concerns, or changes in business requirements. Continuous monitoring also allows teams to improve systems before small problems become larger ones.
Using AI Governance Tools to Automate Routine Work
1. Choosing Tools Based on Business Requirements
AI governance tools can help organizations maintain inventories, record approvals, monitor systems, track risks, and support compliance activities.
However, organizations should not select a tool simply because it offers a long list of features. The right solution should address actual business requirements and fit into existing development, security, data, and compliance processes.
2. Automating Repetitive Governance Activities
Automation can make governance significantly faster. For example, systems can automatically record project information, identify when sensitive information is involved, trigger required reviews, or remind owners when assessments are due.
This allows teams to reserve human judgment for decisions that genuinely require experience and context.
The objective is not to automate every governance decision. Instead, organizations should automate predictable activities and use people where judgment matters most.
Measuring Progress With an AI Governance Maturity Model
Understanding the Organization’s Current Position
Agovernance maturity model can help organizations understand how developed their governance practices are.
n AI
Aearly stage, organizations may have widespread AI usage but limited documentation, ownership, or formal policies. A developing organization may introduce basic inventories, policies, approval processes, and assigned responsibilities.
t an
More advanced organizations can integrate governance into their existing development, security, and business processes.
Moving Toward Continuous Improvement
Mty should not be measured by the number of policies an organization creates. A large collection of documents is not useful if employees do not understand or follow them.
aturi
Are approach focuses on measurable outcomes. Organizations can evaluate whether teams understand their responsibilities, whether high-risk systems receive appropriate reviews, whether incidents are handled effectively, and whether governance processes actually support responsible innovation.
matu
Regular assessments can then identify areas that require improvement.
Implementing AI Governance Without Slowing Delivery
1. Start with Existing AI Systems
Organizations do not need to create a perfect governance program before taking action. A practical starting point is to identify the AI systems already being used across the business.
Teams can create an inventory, identify owners, understand what information each system uses, and classify systems according to risk.
This provides visibility into the current situation and helps leadership identify the areas that require the most attention.
2. Introduce a Small Set of Essential Controls
Organizations should begin with a manageable set of requirements. These can cover data protection, security, testing, documentation, ownership, and monitoring.
Adding too many rules at the beginning can create resistance. It is better to establish essential controls and expand them as the organization gains experience with AI.
3. Integrate Governance Into Existing Workflows
Governance should become part of normal IT operations rather than a separate process that teams have to complete after development.
For example, organizations can incorporate governance checks into project planning, security reviews, testing processes, and release procedures. This makes responsible AI part of everyday delivery.
4. Improve the Process Through Team Feedback
IT teams should have opportunities to explain where governance requirements create unnecessary delays. Leadership can use this feedback to simplify low-risk processes while strengthening controls where actual risks are identified.
This creates a more practical approach where governance evolves alongside technology and business needs.
Building a Sustainable AI Governance Program
1. Treat Governance as an Ongoing Capability
Effective AI governance is not a one-time project. AI technologies, regulations, business processes, and risks continue to change. Organizations therefore need processes that can adapt.
Policies should be reviewed periodically, AI inventories should remain up to date, and responsibilities should be reassessed when systems or teams change.
2. Focus on Enablement Rather Than Restriction
The purpose of governance should be to help teams use AI confidently and responsibly. When employees understand the boundaries, approval requirements, and responsibilities, they can make decisions faster.
A well-designed governance program therefore becomes an enabler rather than an obstacle. It gives developers a clear path for experimentation while protecting the organization from avoidable risks.

Conclusion
AI adoption will continue to expand across IT teams, making effective oversight increasingly important. Organizations do not need to choose between responsible AI usage and fast delivery.
A practical governance approach combines risk-based reviews, clear ownership, simple documentation, appropriate testing, continuous monitoring, and automation. The result is a system that gives teams freedom where the risks are low and stronger controls where the potential impact is greater.
By establishing clear AI governance responsibilities, defining practical AI governance roles, selecting suitable technology, and continuously improving governance processes, IT leaders can create an environment where innovation and accountability work together.
The objective is simple: build enough oversight to protect the organization without creating so much friction that teams stop innovating.
Thememakker helps IT teams build responsible AI solutions with practical governance, secure architectures, and scalable development practices that support innovation, compliance, and faster delivery.
Frequently Asked Questions
-
Q:: What is AI governance?
A:: AI governance is the system of policies, processes, responsibilities, and controls used to manage artificial intelligence responsibly. It helps organizations address privacy, security, fairness, transparency, accountability, reliability, and regulatory expectations.
-
Q:: What are the six pillars of AI governance?
A:: The six commonly recognized pillars are accountability, transparency, fairness, security, privacy, and reliability. Together, they provide a foundation for managing AI systems from development through deployment, monitoring, improvement, and eventual retirement.
-
Q:: What is the best tool for AI governance?
A:: There is no single best solution for every organization. The right option depends on AI usage, risk levels, regulatory requirements, company size, and existing technology. Strong solutions provide visibility, documentation, monitoring, automation, and integration.
-
Q:: What are the best practices for AI governance?
A:: Effective practices include assigning ownership, classifying risks, documenting AI systems, protecting sensitive information, testing outputs, monitoring performance, reviewing changes, educating employees, and maintaining clear procedures for reporting and resolving problems.
-
Q:: How can organizations implement AI governance?
A:: Organizations can begin by creating an AI inventory, assigning owners, classifying risks, defining essential controls, and integrating reviews into existing workflows. They should then monitor outcomes, collect employee feedback, automate routine tasks, and regularly improve policies.
Recommended Posts
97.9%
Projects Delivered On-Time

5,000+
Creatives & Agencies Trust Us.

Development Service?
We can provide at affordable price.


Awwwards, Design Nominees, CSSLight, Best CSS and more




THEMEFOREST
Exclusive Author
Modern Admin Dashboard Templates for Developers & Businesses
Discover professionally designed admin dashboard templates for modern web applications. Our responsive dashboards are built with Bootstrap, React, Vue.js, Angular, Tailwind CSS, Laravel, Next.js, Node.js, ASP.NET, WordPress, WebFlow, and HTML.